Threat & Exposure Intelligence04
MailGuard.AI
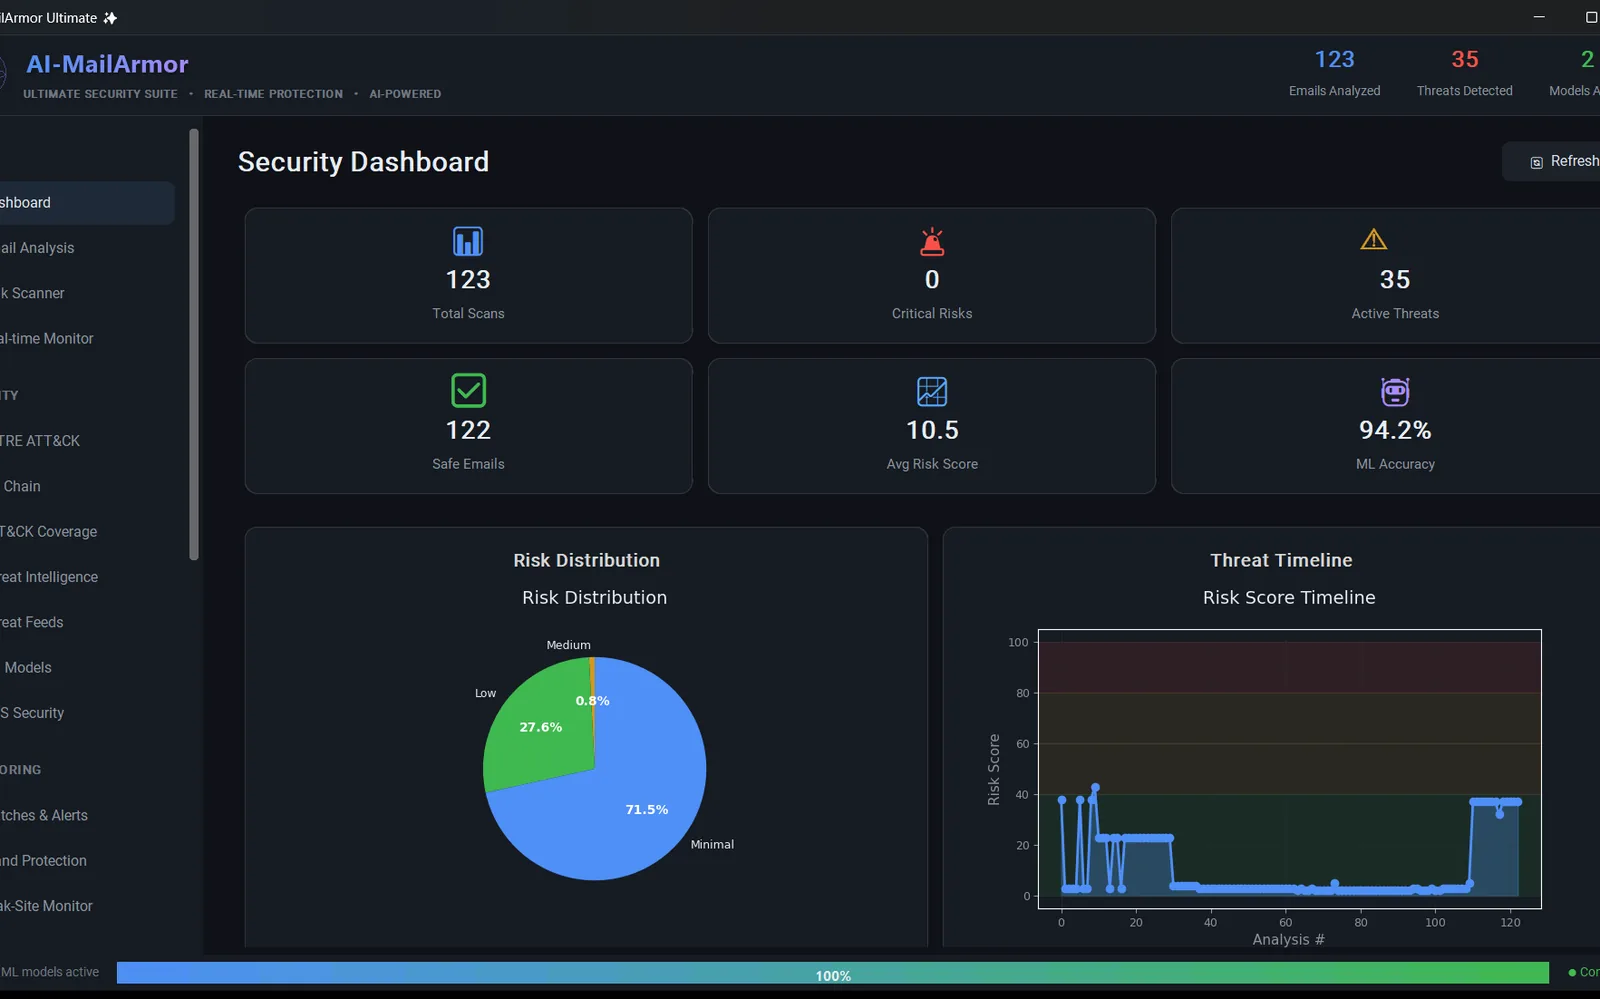
Score any address. Audit any sending domain.
- 27analysis pages in one console
- 679MITRE ATT&CK techniques shipped (local bundle)

Security Operations
From ten thousand alerts to one finished case file.
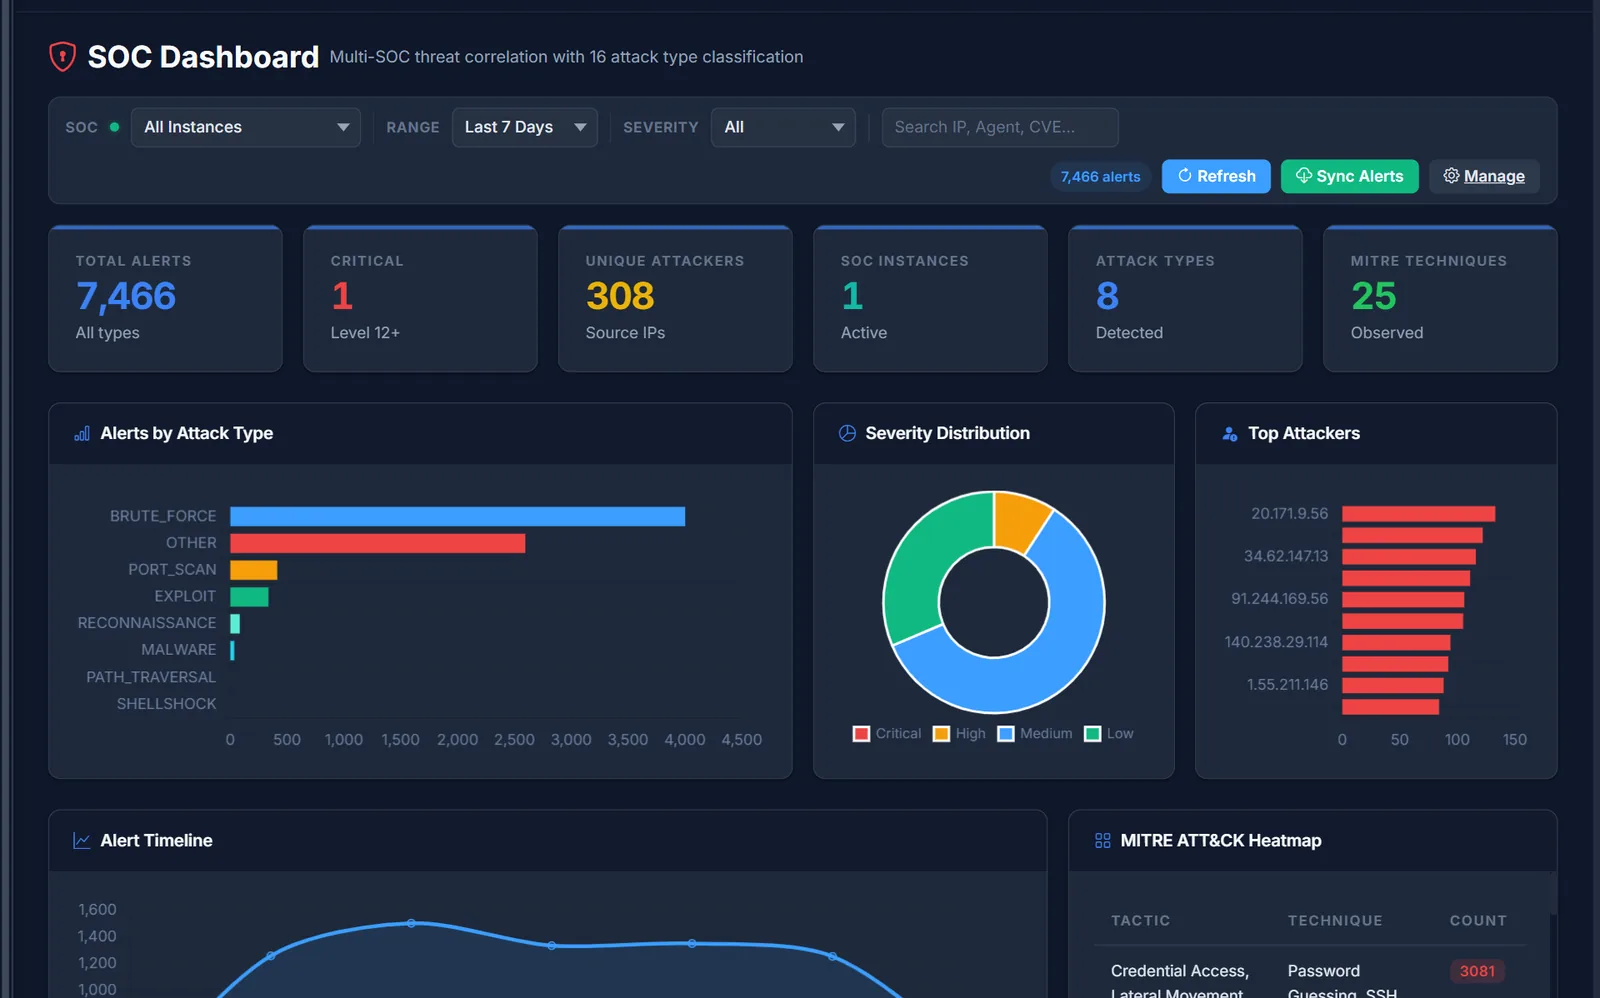
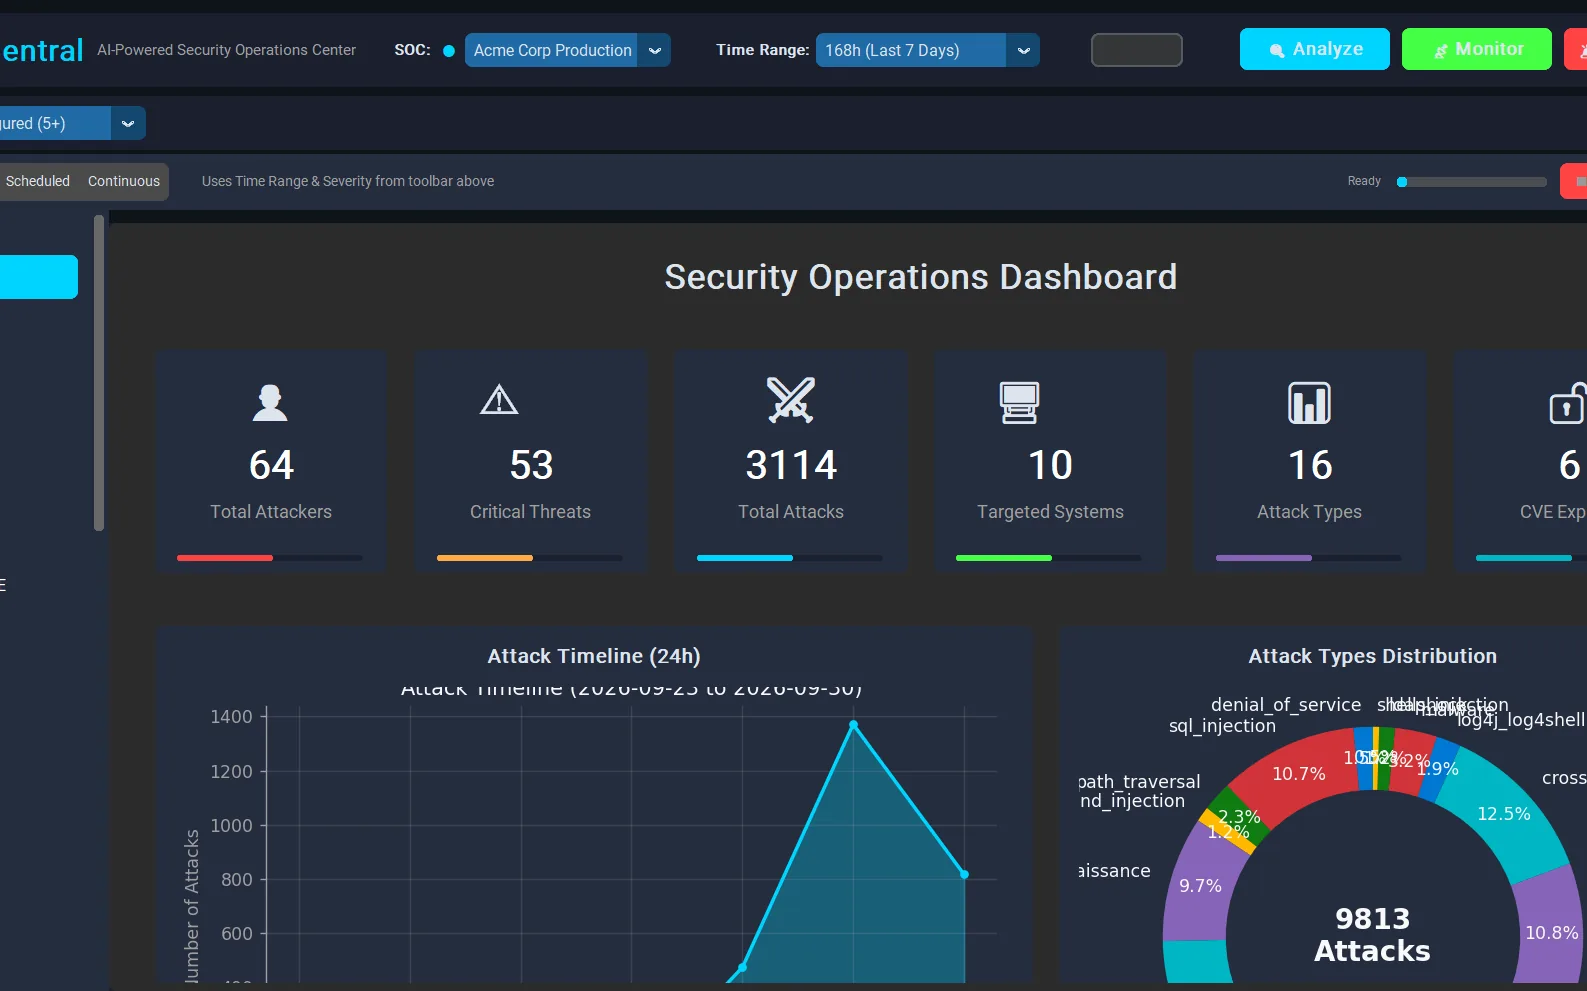
Security operations platform that sits read-only on Wazuh and turns alerts into scored attackers, hashed evidence, framework mapping and board reports.
Why it is different
Turn SIEM alert floods into scored attackers, cases and reports.
Deployment
Windows desktop application (Python / CustomTkinter), read-only towards Wazuh, firewalls and clouds.
Built like every Enyxum Lanka product
Findings are confirmed before they reach you: oracles, live verification, model consensus and precision floors.
Machine learning ranks and corroborates. It never hides a confirmed critical finding, and every score shows why.
Hashes, chain of custody and audit trails are produced as the work happens, not assembled later.
Read-only connectors, encrypted secrets and scoped keys. Products change nothing they do not need to.
Self-hosted or on-premise deployment. Optional enrichment is documented and can be switched off.
Metrics are shown with their method and bounds. Illustrative numbers are labelled and replaced with yours in a pilot.
Works well with
Threat & Exposure Intelligence04
Score any address. Audit any sending domain.
Threat & Exposure Intelligence05
Find everything you own. Report only what you can prove.
Cloud & Server Defense01
One platform. One console. One report.