Investigation & Forensics10
AI-CyberForensix
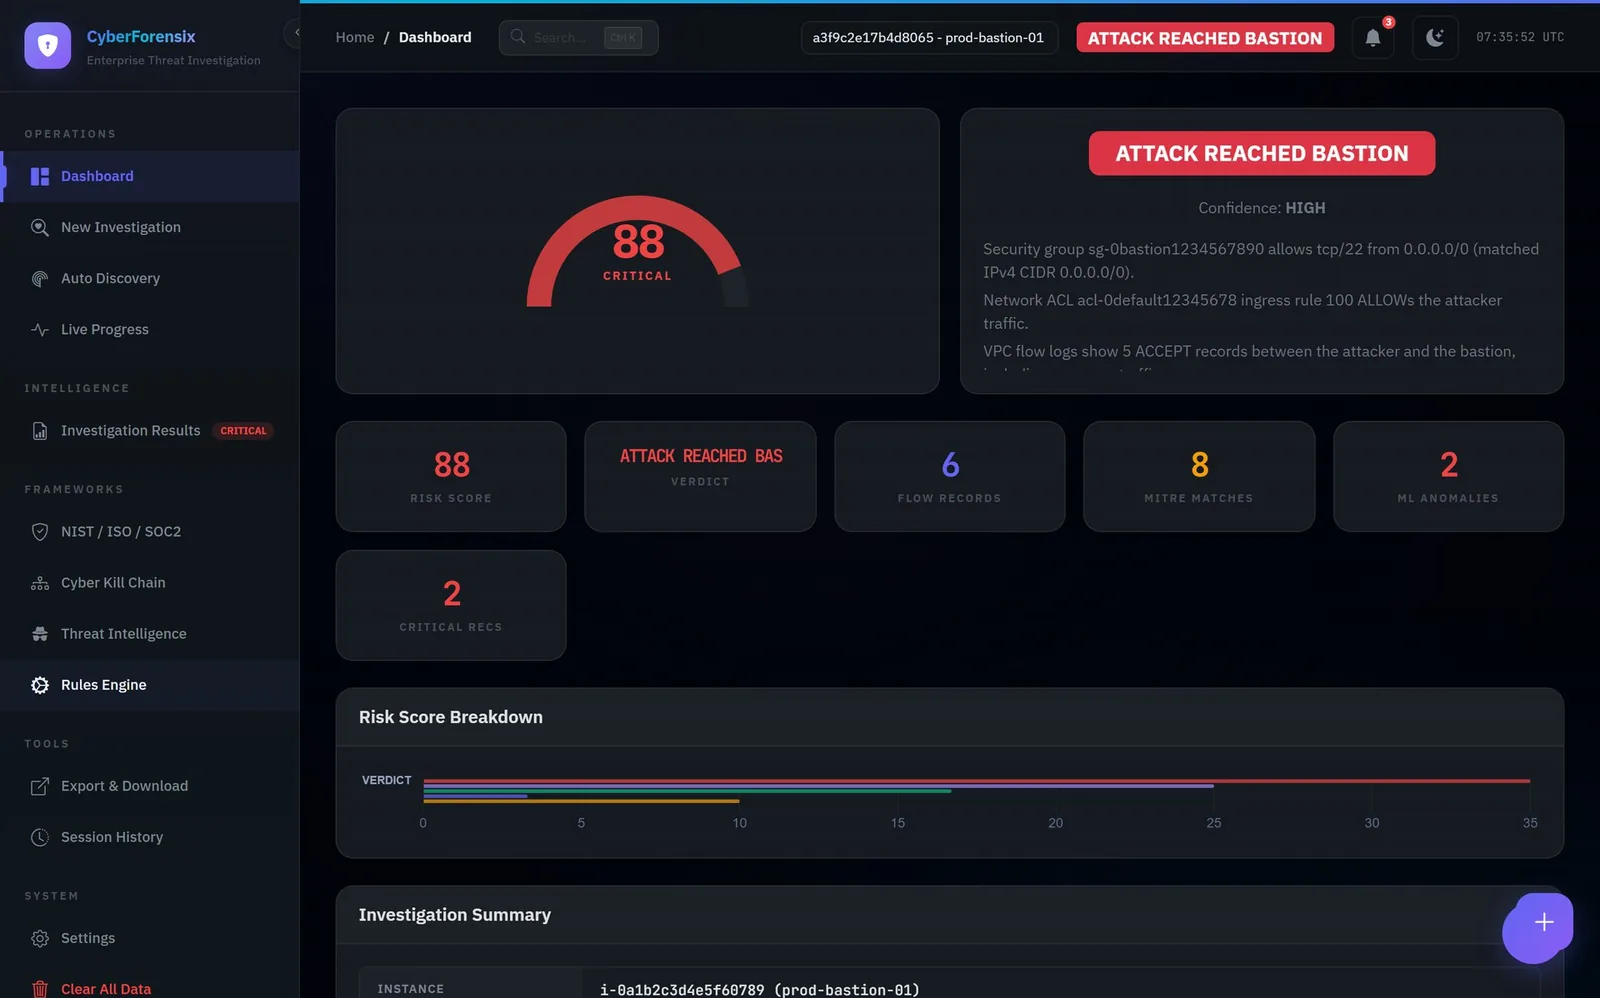
Investigate the attack path. Prove what happened.
- 3cloud providers: AWS, Azure, Google Cloud
- 11investigation steps

Investigation & Forensics
Read the crime scene while it still exists.
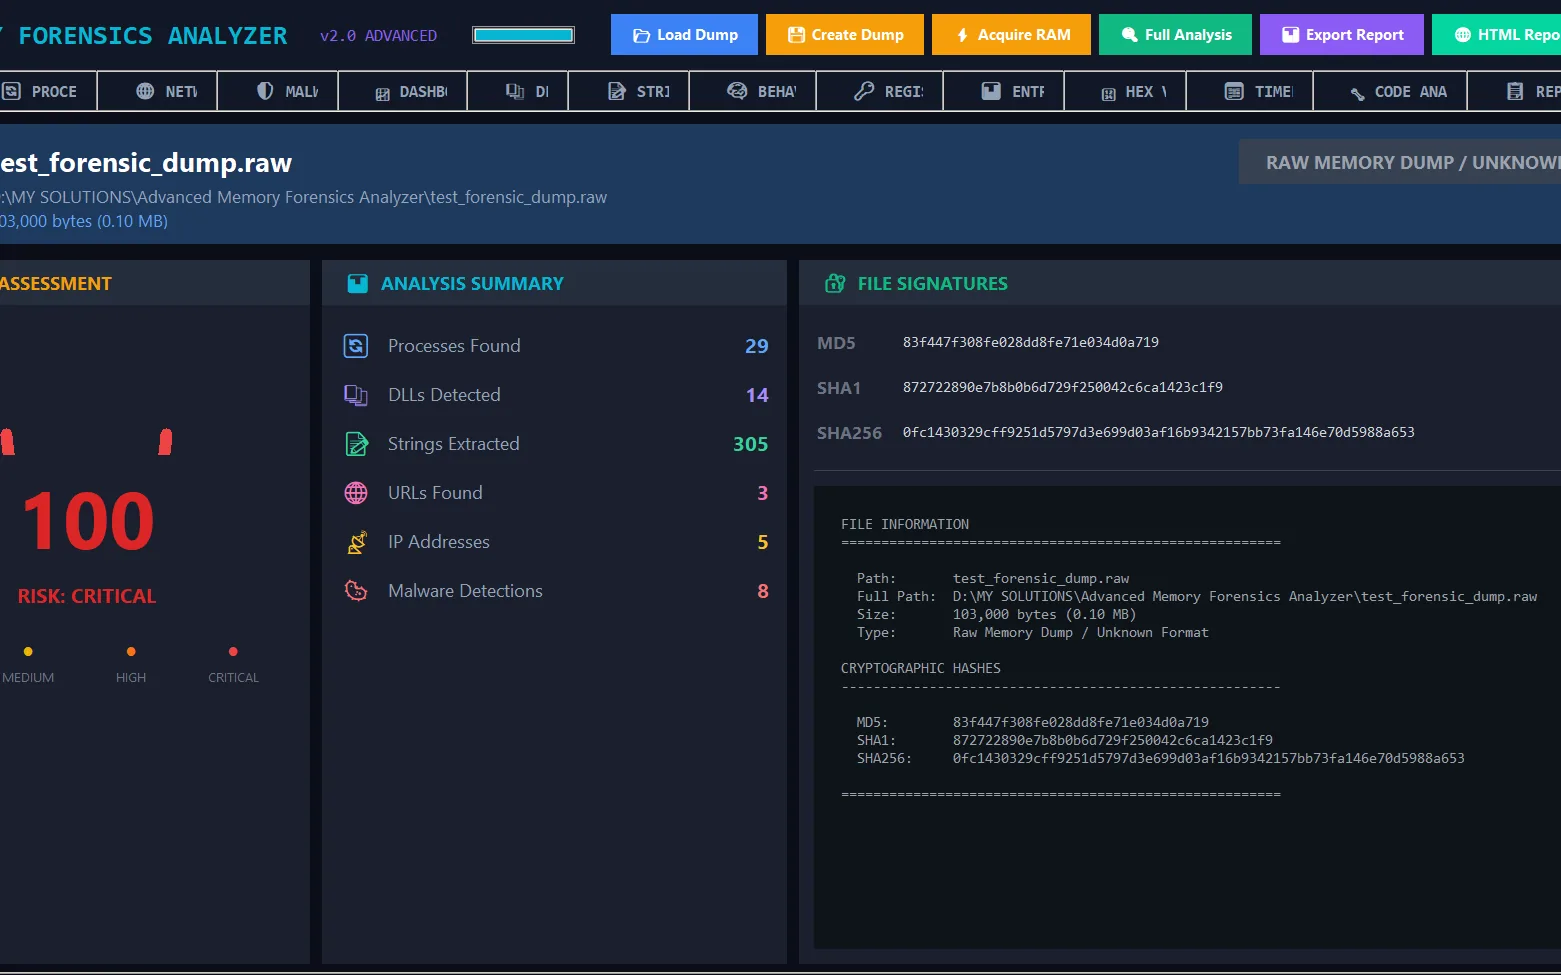
On-premise memory forensics workstation that acquires RAM, detects in-memory malware with four engines, maps behaviour to ATT&CK and writes hashed evidence reports.
Why it is different
Answer what happened, with evidence that holds up: cloud, memory and malware.
Deployment
On-premise Windows desktop application (Python / tkinter) on the forensic workstation; no agent, no cloud.
Built like every Enyxum Lanka product
Findings are confirmed before they reach you: oracles, live verification, model consensus and precision floors.
Machine learning ranks and corroborates. It never hides a confirmed critical finding, and every score shows why.
Hashes, chain of custody and audit trails are produced as the work happens, not assembled later.
Read-only connectors, encrypted secrets and scoped keys. Products change nothing they do not need to.
Self-hosted or on-premise deployment. Optional enrichment is documented and can be switched off.
Metrics are shown with their method and bounds. Illustrative numbers are labelled and replaced with yours in a pilot.
Works well with
Investigation & Forensics10
Investigate the attack path. Prove what happened.
Investigation & Forensics12
Three detection heads. One explainable verdict.
Cloud & Server Defense01
One platform. One console. One report.